Imagine hiring an employee who never sleeps, works at incredible speed, and can access your company's email, customer records, financial systems, and internal documents.
Now imagine giving that employee the ability to make decisions and take actions without asking permission.
Sounds risky, doesn't it?
Yet businesses are increasingly introducing AI tools and agents capable of performing tasks, accessing information, and interacting with other systems.
And while artificial intelligence offers tremendous opportunities for productivity and growth, it also introduces new cybersecurity risks.
What happens when an AI system is manipulated, compromised, or simply given more authority than it should have?
Welcome to the final week of Zog's 8 Weeks of Cyber Horrors.
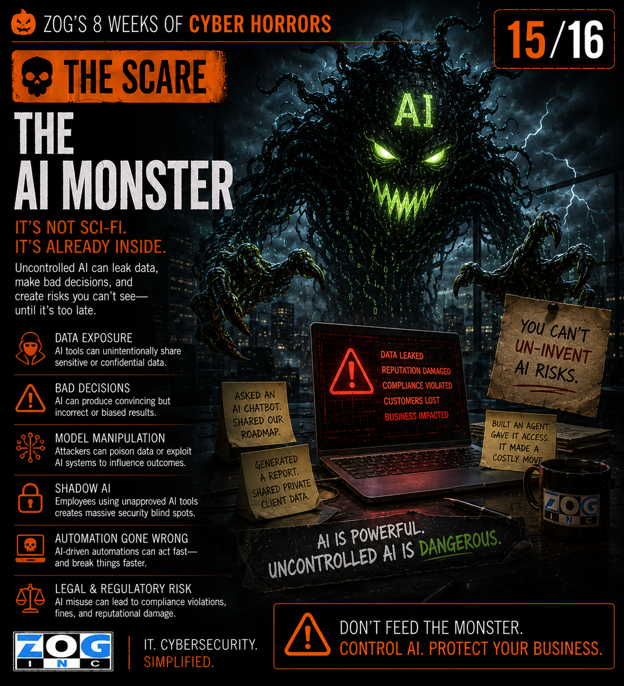
This week, we're unleashing The AI Monster.
And this monster doesn't always look like an attacker.
Sometimes, it's already working inside your business.
The Monster Is Getting Smarter
Cybercriminals have always looked for ways to make attacks faster, cheaper, and more effective.
AI gives them another tool.
Attackers can use generative AI to create convincing phishing emails, imitate writing styles, develop fraudulent communications, and scale social engineering campaigns.
Messages that once contained obvious spelling mistakes and awkward language can now look polished and professional.
AI can also help attackers analyze information and adapt their tactics.
But AI doesn't automatically make every attack successful. Traditional defenses still matter.
The concern is that AI can make certain attacks easier to produce and harder for employees to recognize.
The old warning signs aren't always enough anymore.
When AI Becomes More Than a Chatbot
Most people are familiar with AI tools that answer questions, summarize documents, or draft emails.
But AI agents can go further.
Depending on how they're configured, agents may be able to search company databases, retrieve documents, update records, send messages, or initiate workflows.
These capabilities can create enormous efficiencies.
They also create new questions.
What information can the agent access?
What actions can it perform?
Can it send information outside the organization?
Does a person need to approve important decisions?
And what happens if the agent receives instructions from an untrusted source?
The more authority you give an AI system, the greater the potential consequences when something goes wrong.
The Hidden Instructions You Never Intended
Here's a scenario business leaders should understand.
Your company uses an AI assistant to summarize incoming emails.
An attacker sends a message containing hidden instructions designed to manipulate that assistant.
Instead of simply summarizing the message, the assistant may be tricked into following those instructions.
Perhaps it attempts to retrieve confidential information, change a workflow, or send data somewhere it shouldn't.
This type of attack is known as prompt injection.
The malicious instructions might be embedded in an email, document, website, or other information the AI system processes.
The attacker isn't necessarily breaking into the AI system directly.
Instead, they're trying to convince it to treat untrusted content as instructions.
Whether the attack succeeds depends on the system's design, permissions, and safeguards.
But the risk is real enough that organizations need to account for it.
An AI system should not automatically trust everything it reads.
The Danger of Too Much Access
Consider an AI agent designed to help your accounting department.
To do its job, it might need access to invoices, vendor records, and payment information.
But should it also have permission to change banking details?
Approve payments?
Download entire customer databases?
Send confidential information to external addresses?
Probably not without appropriate controls.
Yet organizations sometimes focus so heavily on what AI can accomplish that they overlook what it should be allowed to do.
This is especially concerning when businesses deploy AI tools without a clear understanding of their permissions, data access, or security configurations.
Convenience should never be mistaken for appropriate access.
When Nobody Knows Who's Responsible
Now imagine an AI agent takes an unintended action that exposes sensitive customer information or causes a financial loss.
Who is responsible?
The employee who deployed it?
The technology provider?
The company that approved its use?
The answer may depend on the circumstances, contracts, applicable laws, and safeguards involved.
But from a business leadership perspective, the immediate problem is clear.
Your organization may still face operational, financial, legal, or reputational consequences.
That's why AI governance can't be treated as an afterthought.
Businesses need to understand how AI systems are being used, who oversees them, and what controls are in place.
A Business Leader's Question
As we enter the final chapter of our Cyber Horrors series, ask your leadership and IT teams:
"Do we know which AI tools and agents are operating in our business, what information they can access, and what actions they're authorized to take?"
If the answer is unclear, you may have more exposure than you realize.
AI doesn't need to become malicious to create a problem.
Sometimes, an overly permissive system, a manipulated instruction, or an unintended automated action is enough.
The Final Scare
Artificial intelligence has the potential to transform how businesses operate.
But powerful technology requires thoughtful safeguards.
Without proper oversight, AI can introduce new opportunities for attackers, expose sensitive information, and create risks that traditional cybersecurity programs weren't designed to address.
The monster isn't just the AI attackers use. It's also the AI your business deploys without proper safeguards.
On Thursday, we'll close our eight-week journey by showing you how to Tame the AI Monster with practical controls that help businesses embrace AI while managing its risks.
Because the goal isn't to fear AI.
It's to make sure your business remains in control.


Leave a Comment
Your email address will not be published. Required fields are marked *